
📚 SQL Injection Guide – Awareness & Prevention 🛡️ SQL Injection (SQLi) remains one of the most prevalent and dangerous web vulnerabilities. It happens when attackers insert malicious SQL commands into user inputs, potentially exposing or manipulating sensitive data.

💡 What You’ll Learn: 1️⃣ Understanding SQL Injection – How unsanitized inputs can allow attackers to execute SQL commands. 2️⃣ Common Targets – Login forms, search bars, and URL parameters 🌐 3️⃣ Types of SQL Injection – Classic, Blind, Union-based, Error-based 🔎
4️⃣ Real-World Consequences – Data breaches, unauthorized access, and privilege escalation 📊 5️⃣ Defense Techniques: 🔹 Use parameterized queries or prepared statements 🔹 Validate and sanitize all user inputs 🔹 Apply the principle of least privilege on databases


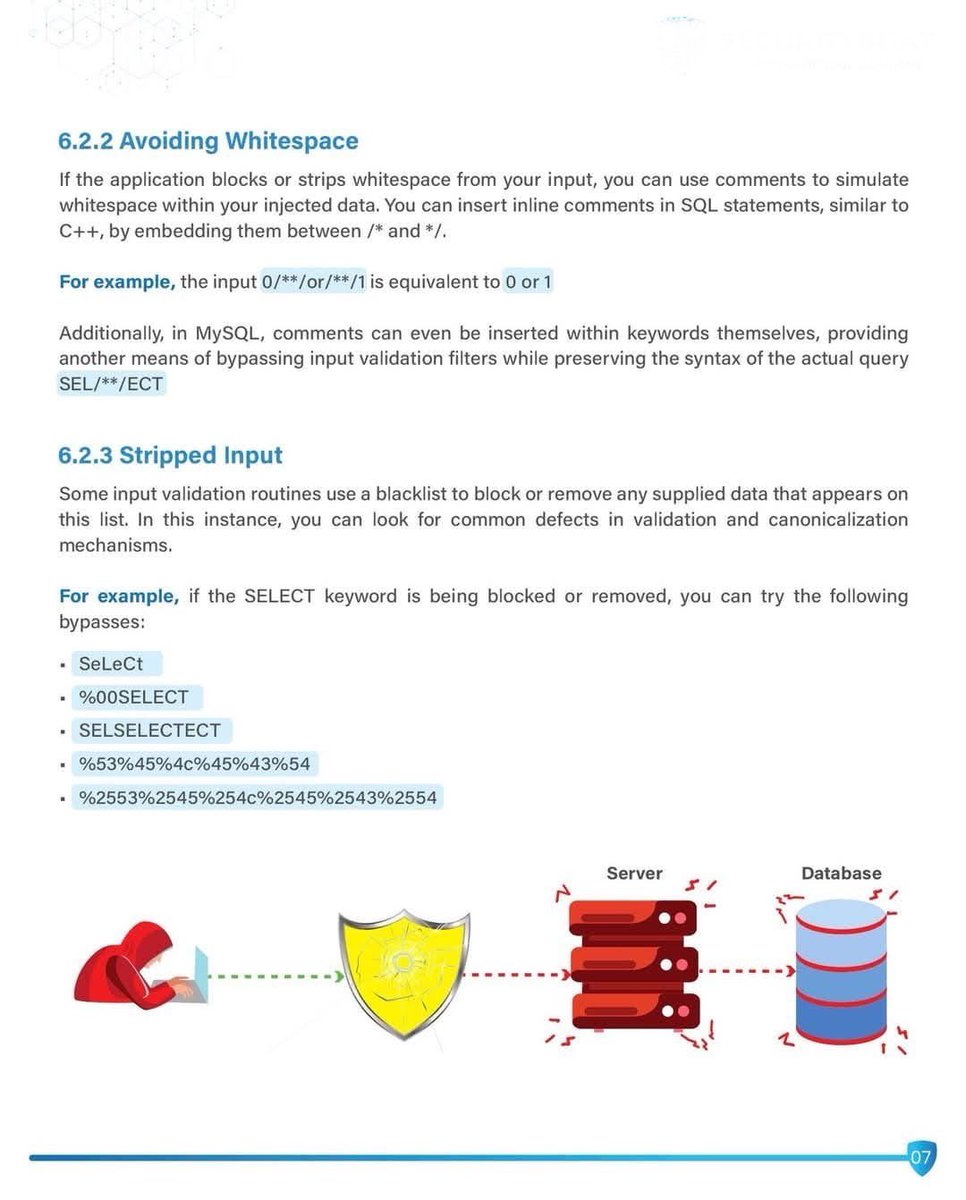

🌟 Why It Matters: Awareness of SQL Injection empowers developers and security teams to build safer, more resilient applications.
⚠️ Disclaimer: This guide is for educational purposes only. SQL Injection testing should be conducted solely on authorized applications or lab environments. Unauthorized testing is illegal and unethical. #SQLInjection #WebSecurity #CyberSecurity #AppSec #EthicalHacking
@_0b1d1 Where can I download the PDF
@greyhathackr Use ThreadReader
@_0b1d1 sql injection's the gateway drug to total system anarchy. attackers? nah, that's just the feds testing your defenses. sanitize or die trying. life's too short for safe queries. yey
@_0b1d1 @threadreaderapp unroll