
🚨 TEEs just have been fully compromised 🚨 TLDR; A new exploit makes TEEs fully exploitable. Many crypto "privacy" projects used them. TEEs don't bring privacy or security. Our <encrypted> computing is the only solution. All you need to know 🧵👇

2/ TEEs promise: Build hardware that can process information without anyone (not even the operator!) seeing it to gain privacy and security. Reality: It's failed in the past and with today's brutal exploit has reached it's peak of failure. After billions were poured into this.
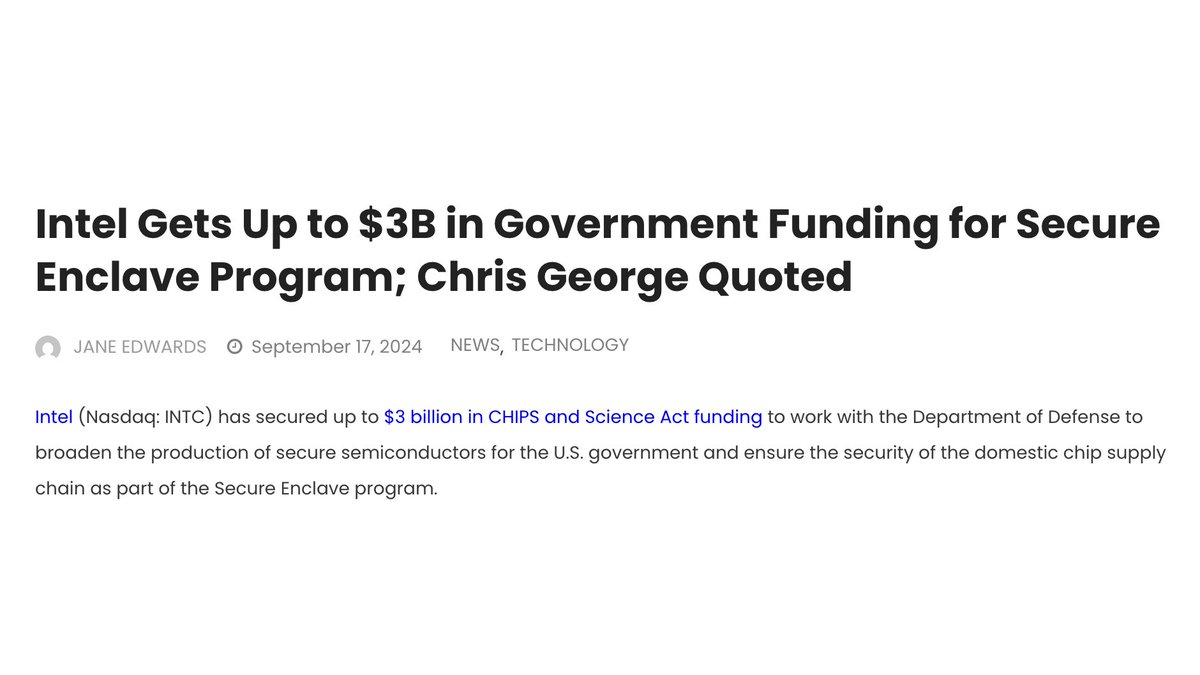
3/ Today's exploit is brutal💀 Given physical access, anyone can completely break Intel SGX, Intel TDX and AMD SEV‑SNP. Even a hobbyist-level attacker can extract attestation keys and enclave secrets. The paper demonstrates real attacks on blockchains. TEEs in crypto are done.
4/ Consequence: when node operators or strangers have physical access (as they do in permissionless, decentralized systems), TEEs cannot guarantee any level of privacy or integrity. They are the polar opposite of trustless. They bring a invalid claim of security.
5/ Many cloud vendors already note physical attacks are out of scope. But many production deployments ignore that caveat in practice. The trust model is fundamentally flawed.
6/ Cheap DRAM-bus interposition let's anyone extract anything. The attack literally only costs about $10 and requires no deep technical skillset. If you want to learn more about how it works, you can read the full Wiretap exploit here: https://wiretap.fail/

7/ I have long been outspoken about this. So many teams in crypto claim to build privacy but are actually just SGX, TDX or SEV‑SNP wrappers. Worthless technology. Worthless wrappers. Zero value.

8/ So what is the alternative? Cryptography. Cryptography has always been the only solution. More specifically, <encrypted> computing.
9/ Over the last year, the @ArciumHQ team has been working on the Cerberus MPC protocol. The only trustless and scalable encrypted computing protocol in the world. The first practical dishonest majority protocol.

10/ Instead of giving your data to some exploitable TEE, Cerberus executes over the encrypted data across an arbitrary number of nodes. As long as there exists just 1 single honest node, doesn't matter which, everything is private. The first practical dishonest majority protocol
11/ Our Cerberus MPC protocol additionally is highly scalable. We already achieve multiple orders of magnitude higher throughput than any other protocol out there. This is the encrypted supercomputer. A trustless encrypted execution engine that processes at the speed of light.
12/ Final thoughts: I told you so. TEEs are dead. There is a reason why you need a team of the most experienced cryptography PhDs in the world to build what we're building. Or as @deanmlittle put it: "TEEs are, and always have been, a retarded idea"

@yrschrade > TEEs just have been fully compromised What the fuck are you talking about? You either didn’t read the papers or can’t comprehend their contents. This isn’t a general break on TEEs conceptually. You should be helping advance privacy not FUDing. “Mr. CEO” Embarrassing.
@JohnAlanWoods Pretending that TEEs are secure is embarrassing. People should take Eli-Ben Sasson's advice, and never touch them with a 10 foot pole.
@yrschrade Did you read the paper before posting? It's SGX + DDR4 only, these are antiquated systems. Anyone can tell you this. Anyone serious has been running TDX. DDR5 has been a go-to option for the last 3 years at least. Surprised to see such a bad faith post.
@candyflipline TDX uses the same deterministic encryption. As the authors have written, all you need is a PoC for DDR5. In my mind this is bad. That being the only defense in a permissionless adversarial setting to manage billions of assets is insane imho.
@yrschrade nice thread sir.. but I think saying TEE is worthless is a bit far no? isnt the verifiable/attestation still useful? like sure its dog shit for privacy.. but sometimes its good for verifiability. like sometimes creating a validity proof is too taxing. gMPC
@kyle_corsola worth less than what folks pretend it's worth
@yrschrade I’ve said this from day 1: TEEs will end where TPM ended. Relying on them is risky. Starkware never would touch them with a 10 foot pole
@EliBenSasson That's my Cypherpunk💜
@yrschrade I thought this exploit was validated against the sgx enclaves only. Not sure how we are generalising it for TDX and SEV enclaves without proper experimentation.
@sudeepskamat TDX and SEV-SNP just like SGX rely on memory encryption engines with deterministic counter/nonce generation tied to physical addresses. Different implementations but same core flaw. This is what was exploited.
@yrschrade tl;dr - don't be a TEEtard
@_arihantbansal Yes. Be smart, don't be a TEEtard.
@yrschrade Interesting read...how comes nillion are both in the Tee section and MPC section. Are they save to use?
@dak_shado They use TEEs for execution, which is what is affected by the exploit. MPC only for data storage.
@yrschrade My face while reading this.
@kru_tweets My face while writing this.

@yrschrade Reject TEEs embrace MPC
@Cryptanzee embrace MPC
@yrschrade link to the news article?
@chainyoda WireTap exploit website: https://wiretap.fail/