
Just caught a pretty nasty bug in my software renderer with clang -fsanitize=undefined. Who needs Rust really? Learn clang sanitizers - they are awesome!

Oh hey, look! Forgot to pad some data in my assets packer! No worries, UBSan got my back! And it doesn't yell at me. Just politely pointing out things without introducing any friction. :)
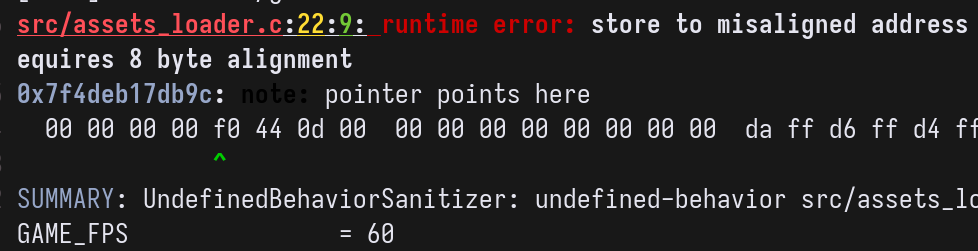
ez fix

@tsoding "who needs rust!" *shows runtime memory error* Believe me I always use -fsanitize=addresss,undefined,leak but lets not pretend a few mutually exclusive runtime sanitizers is a full replacement
@lispexmachina Rust checks this kind of problem at runtime too

@tsoding I've tested both GCC and Clang on 7 bugs / memory errors and I've found GCC to be my preferred compiler as its static analyzer is more powerful compared to Clang. https://hwisnu.bearblog.dev/ma... All 7 were caught by GCC static analyzer at compile time, which is amazing.

@handikawisnu Oh yeah, I should check out what GCC has to offer. Thank you!
@tsoding Bro finds a new reason to hate on Rust every day
@tsoding It could be argued that it is better to find most issues in compile time.
@tsoding That’s the kind of debugging power people sleep on. Clang’s sanitizers catch the monsters hiding in C/C++ code before they wreck your weekend. Not Rust-level safety, but close enough for the brave and it makes you a sharper engineer.
@tsoding Wow!
@tsoding but what else is hiding there, uncaught, lurking around, waiting for its chance to crash the program?
@tsoding It can not detect all mistakes, for example it can not detect missmatch pointer cast
@tsoding Yeah, i suspect too, that C code + compile-time/runtime checks > Rust
@tsoding Related: On Windows, this command will give the full path of ASAN shared lib: `clang -print-file-name=clang_rt.asan_dynamic-x86_64.dll` Make sure to copy this file to the same directory as thr executable
@tsoding Typical problem with C when nothing works by default and you have to babysit everything
@tsoding Sanitizers are great, I use them heavily, I fixed 100s of if not 1000s bugs with it. But it has some serious use issues: - only catches bug at runtime, - you need 100% code coverage and right TCs - Adds extra overhead at runtime(significant) - all does not work together
@tsoding Am so dumb,I don't even have an idea what you talking about.
@tsoding best tools for debugging
@tsoding Just one more compiler flag bro, I promise, just one more flag bro and it will all be fine.
@tsoding You’re right, sanitizers are criminally underrated. Caught more real bugs with -fsanitize than most people do with type systems
@tsoding Even "-O3 -Wall" can find many kinds of bugs spanning over a dozen stack frames, sanitizers on top of that are just awesome
@tsoding I should try this with my C programs, I use -fsanitize=address sometimes to check for malloc and no free
@tsoding Maybe they should be enabled by default, you know because people
@tsoding Why would you use a language where you have to explicitly enable a feature called "find the bugs in my program"? Rust gives it to you out of the box...
@tsoding Cross compilation, all warnings with GCC/Clang/MSVC really is the way imho. Catch everything you can, run all the exec with test tools.
@tsoding thread sanitizers not bad also
@tsoding Rust is useless.
@tsoding 🦀